
Services / Managed Compliance & Executive Services
Managed Compliance · Internal Audit
Independent internal audits, on a schedule you can rely on
Planned internal audits for ISO/IEC 27001, 42001, 27701, ISO 22301, ISO 9001, ISO 14001 and ISA/IEC 62443 programmes, with continuous compliance monitoring.
How an engagement runs
- PlanProgramme and schedule
- AuditInterviews, records, sampling
- ReportFindings and recommendations
- CorrectRoot cause and actions
- Follow upVerify effectiveness
Nothing left unaudited
Every control audited across the certification cycle.
A good internal audit finds the problem before the certification auditor does, and helps fix the cause, not the symptom.
Dr. Sanjay Vaid, Invocore
Stay audit-ready all year
Certified organisations must run internal audits and management reviews. Our auditors carry out them independently, report findings clearly and help you close them before surveillance or recertification audits.
The challenge
Why this matters now
Every certified management system needs internal audits, but many organisations struggle to run them well. Internal auditors may lack independence or experience, audits slip behind schedule, and the same findings return year after year.
Our internal audit service provides experienced, independent auditors on a planned schedule. We audit against the standard and your own procedures, report clearly, and help you close findings at the root cause, so external audits hold no surprises.
Certification requirements
ISO management system standards require planned internal audits and management review.
More standards to manage
Many organisations now run several management systems at once.
Resource constraints
Experienced internal auditors are hard to recruit and retain.
Quick self-check
How ready are you?
Answer four questions leaders ask us. Your result appears instantly; nothing is stored or sent.
Is every clause and control audited over the certification cycle?
Are our internal auditors truly independent?
Do findings get closed, or do they repeat?
Are we ready for the next surveillance audit?
What we deliver
Capabilities
Annual audit programme
A risk-based plan covering every clause and control over the cycle.
Independent audits
Experienced auditors with no role in running your system.
Clear reports
Findings graded by significance with practical recommendations.
Corrective action support
Root-cause analysis and follow-up until findings are closed.
Management review input
Audit results ready for your management review.
Multi-standard
One audit programme across several management systems.
Interactive
Explore the framework
Select any part of the diagram to see what it covers.
Selected
Plan
A risk-based audit programme covering every clause and control.
Audit
Interviews, record reviews and sampling by independent auditors.
Report
Clear findings graded by significance, with recommendations.
Correct
Root-cause analysis and corrective actions.
Follow up
Verify that actions were effective and close findings.
Our approach
How we work with you
A clear, staged path from first assessment to lasting capability.
Step 1
Plan
Programme and schedule
Step 2
Audit
Interviews, records, sampling
Step 3
Report
Findings and recommendations
Step 4
Correct
Root cause and actions
Step 5
Follow up
Verify effectiveness
Why Invocore
What sets us apart
Senior, practitioner-led advice that holds up in front of auditors, boards and customers.
Experienced lead auditors
Audits led by auditors who know how certification bodies assess.
Integrated audits
One programme across ISO/IEC 27001, 42001, 27701, ISO 22301, 9001, 14001 and 62443.
Findings that close
Root-cause analysis and follow-up until corrective actions are effective.
Engagement models
Start where you are
Begin with a focused first step and expand as value is proven.
Quarterly
Four audit visits each year across your scope.
Fees on enquiry
Half-yearly
Two audit visits each year.
Fees on enquiry
Annual
One full internal audit each year.
Fees on enquiry
Deliverables
What you receive
- Risk-based annual audit programme
- Audit plans and checklists
- Audit reports with graded findings
- Corrective action tracker
- Management review input summary
- Pre-certification readiness review
Outcomes
What changes for you
- A risk-based audit programme across your management systems
- Independent audits with clear, graded findings
- Corrective actions closed at the root cause
- Confidence going into every external audit
Who we work with: ISO-certified organisations, Companies preparing for certification, Multi-site organisations and Groups with several management systems.
Frequently asked questions
Can you audit several standards together?
Yes. Integrated audits save time for your teams.
Can the same consultant who implemented our system audit it?
For independence, internal audits are carried out by an auditor who did not implement the area being audited.
Is this the certification audit?
No. Certification audits are performed by an independent accredited certification body.
Client success story
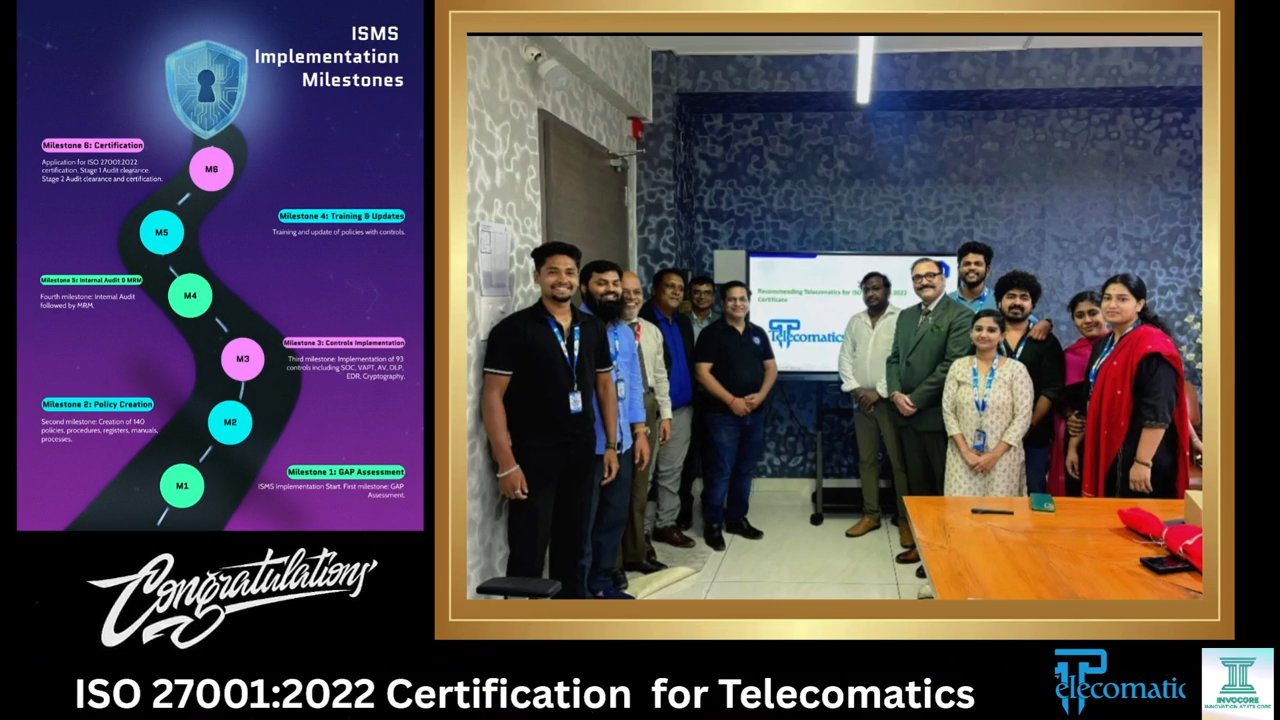
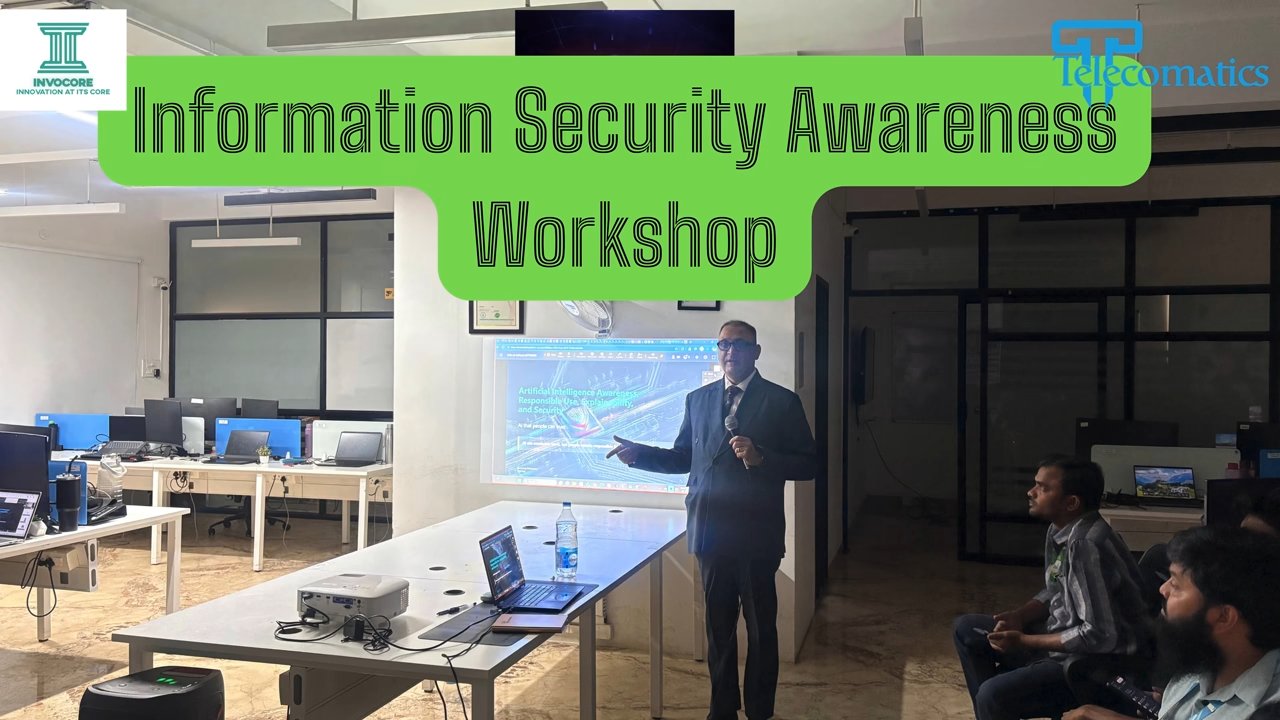
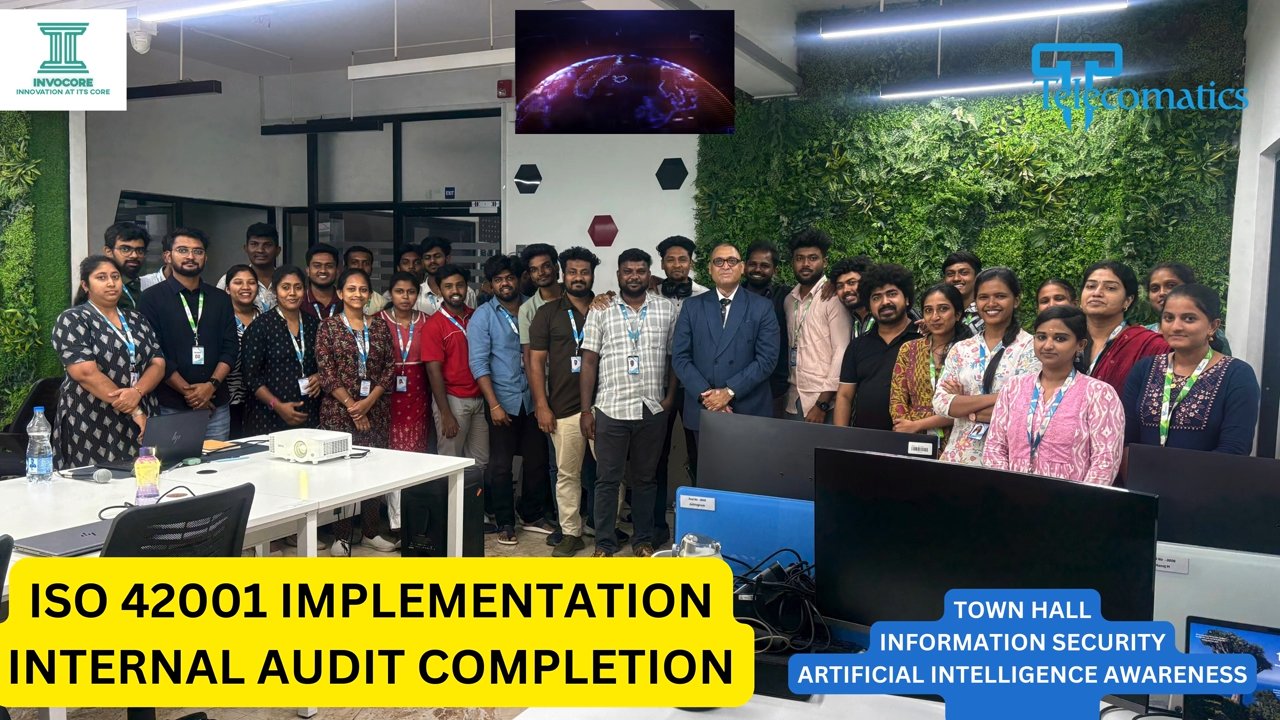
Telecomatics Technologies: from ISO 27001 certification to responsible AI
A technology company in Coimbatore, India, working with Invocore across consulting, implementation, internal audit and training. Information security came first; ISO/IEC 42001 AI governance followed on the same foundations.
- ConsultingISMS kickoff and a full gap assessment against ISO/IEC 27001:2022.
- ImplementationMore than 140 policies, procedures and registers, built with the team.
- CertificationISO/IEC 27001:2022 certification by an NABCB-accredited certification body.
- Internal auditOngoing quarterly internal audits to keep the ISMS effective.
- AI governanceISO/IEC 42001 AI management system implemented and internally audited.
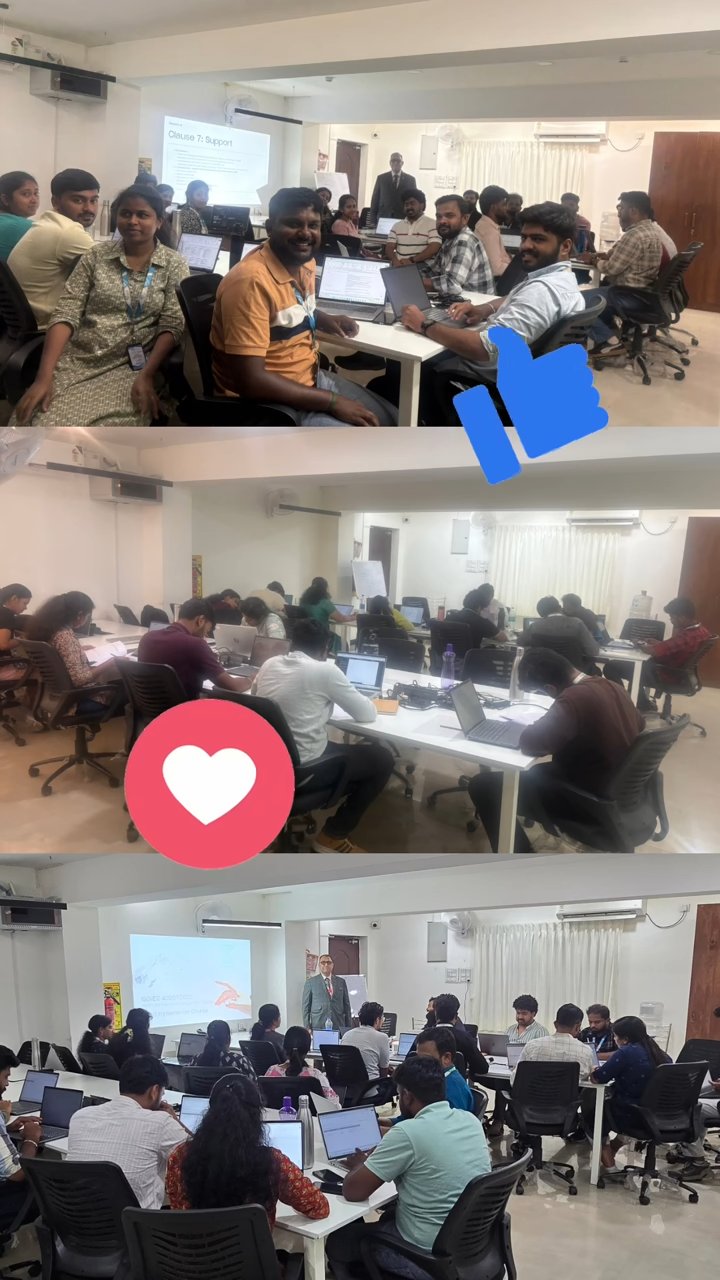
- TrainingISO/IEC 42001 Lead Implementer and Lead Auditor programmes, plus awareness for all staff.
Get in touch
Discuss your requirement
Tell us about your organisation and goals. A senior consultant will reply, usually within one working day.
Prefer to talk now? WhatsApp +91 98108 17659 or info@invocore.org
