
Services / Consulting & Implementation
ISO/IEC 27001 · Information Security
Build an ISMS that works, and pass certification with confidence
End-to-end ISO/IEC 27001:2022 implementation: scope, risk assessment, Annex A controls, documentation, internal audit and certification-audit support.
93 controls, chosen by risk
ISO/IEC 27001:2022 Annex A: 93 controls in four themes, applied where your risks call for them.
Certification is the milestone, not the goal. The goal is a security system that keeps working after the auditor leaves.
Dr. Sanjay Vaid, Invocore
Information security your customers can trust
Customers, regulators and partners increasingly ask for ISO/IEC 27001 certification. We help you build an information security management system that fits how your business really works, not paperwork for its own sake.
The challenge
Why this matters now
Most organisations already do many of the right things on security: firewalls, access controls, backups. What they often lack is the system around them, the scope, risk method, ownership, evidence and review that turn individual controls into a management system an auditor and a customer can trust.
ISO/IEC 27001:2022 provides that system. Done well, it becomes a competitive advantage: shorter security questionnaires, faster enterprise sales cycles and a leadership team that understands its information risk. Done badly, it becomes a binder of documents nobody reads. Our work is about making sure it is the former.
Customer due diligence
Enterprise customers and global clients increasingly require ISO/IEC 27001 certification before awarding contracts.
The 2022 revision
The updated standard reorganised Annex A into 93 controls and introduced new topics such as threat intelligence and cloud services.
Regulation and data protection
Requirements such as India's DPDP Act raise expectations for security safeguards around personal data.
Quick self-check
How ready are you?
Answer four questions leaders ask us. Your result appears instantly; nothing is stored or sent.
Which information assets would hurt us most if they were exposed?
Are our controls designed around our real risks or a template?
Will our teams follow the policies we write?
Are we ready for the certification audit, and the surveillance audits after it?
What we deliver
Capabilities
Scope and context
Define what the ISMS covers and the requirements of interested parties.
Risk assessment and treatment
A practical risk method, risk register and Statement of Applicability.
Annex A controls
Organisational, people, physical and technological controls that fit your environment.
Policies and procedures
Concise documents your teams will actually use.
Awareness training
Short sessions so every employee knows their part.
Internal audit and management review
Independent internal audit and readiness for the certification audit.
Interactive
Explore the framework
Select any part of the diagram to see what it covers.
Selected
Plan
Set scope, assess risks and choose controls in the Statement of Applicability.
Do
Implement controls, policies, training and operational processes.
Check
Monitor, measure and run internal audits and management reviews.
Act
Correct nonconformities and continually improve the ISMS.
Our approach
How we work with you
A clear, staged path from first assessment to lasting capability.
Step 1
Understand
Business context and scope
Step 2
Assess
Gaps and risks
Step 3
Implement
Policies and controls
Step 4
Build
Awareness and competence
Step 5
Validate
Internal audit and review
Why Invocore
What sets us apart
Senior, practitioner-led advice that holds up in front of auditors, boards and customers.
Practical, not paperwork
Lean documentation built around how your teams actually work.
Audit-ready by design
An experienced lead auditor shapes the system, so evidence is collected from day one.
One partner, full journey
Gap assessment, implementation, training, internal audit and certification support in one engagement.
Engagement models
Start where you are
Begin with a focused first step and expand as value is proven.
Assess
Fixed-scope gap assessment against ISO/IEC 27001:2022 with a prioritised plan.
Fees on enquiry
Implement
Full implementation through to certification-audit readiness.
Fees on enquiry
Sustain
Ongoing internal audits, surveillance-audit preparation and improvement.
Fees on enquiry
Deliverables
What you receive
- Scope statement and context analysis
- Information security policy and objectives
- Risk assessment methodology and risk register
- Statement of Applicability
- Policies, procedures and records
- Awareness training for staff
- Internal audit report and management review pack
Outcomes
What changes for you
- A scoped ISMS that fits how the business runs
- A risk register and Statement of Applicability you can defend
- Policies people use, with clear owners
- Readiness for certification and every audit that follows
Who we work with: IT and SaaS companies, BFSI and fintech, Healthcare, Manufacturing, BPO and services and Startups preparing for enterprise customers.
Frequently asked questions
How long does ISO 27001 implementation take?
It depends on size and scope. A focused scope for a small organisation can be ready in a few months; larger scopes take longer.
Do you also certify us?
No. Certification is carried out by an independent accredited certification body. We prepare you for that audit.
We already have some security controls. Do we start from scratch?
No. The gap assessment shows what you already have and what is missing, so effort goes where it is needed.
Client success story
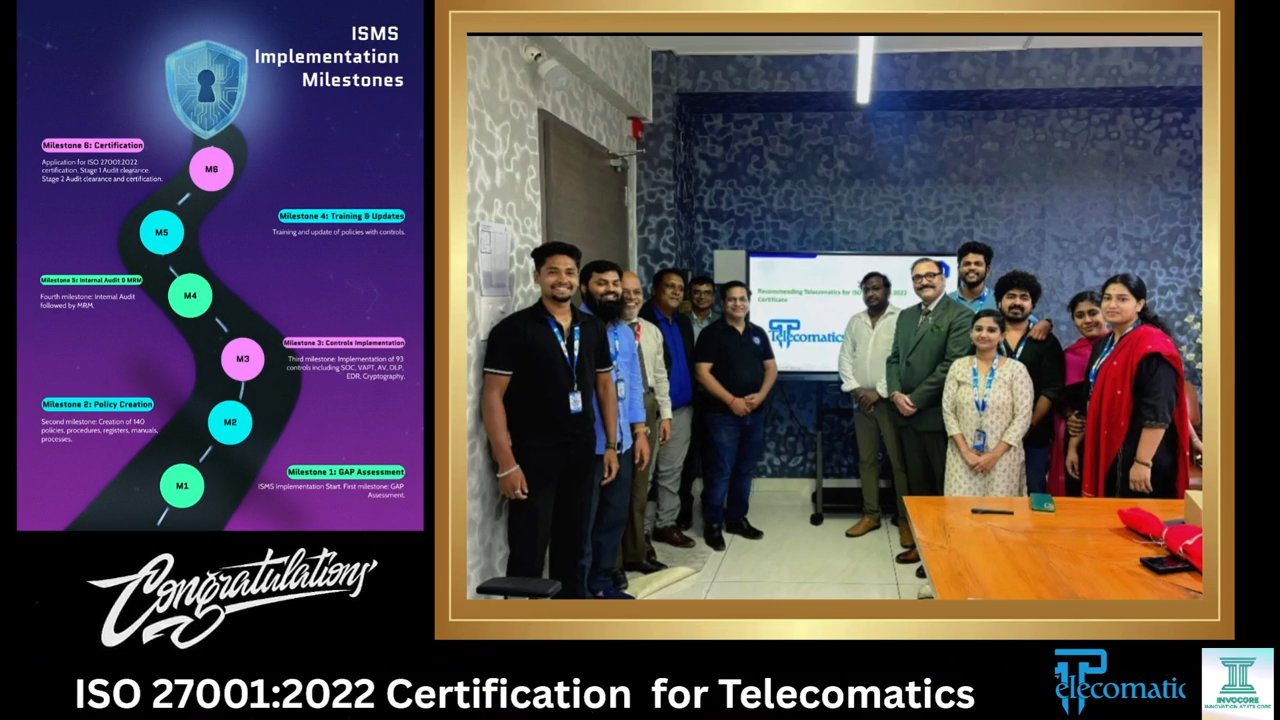
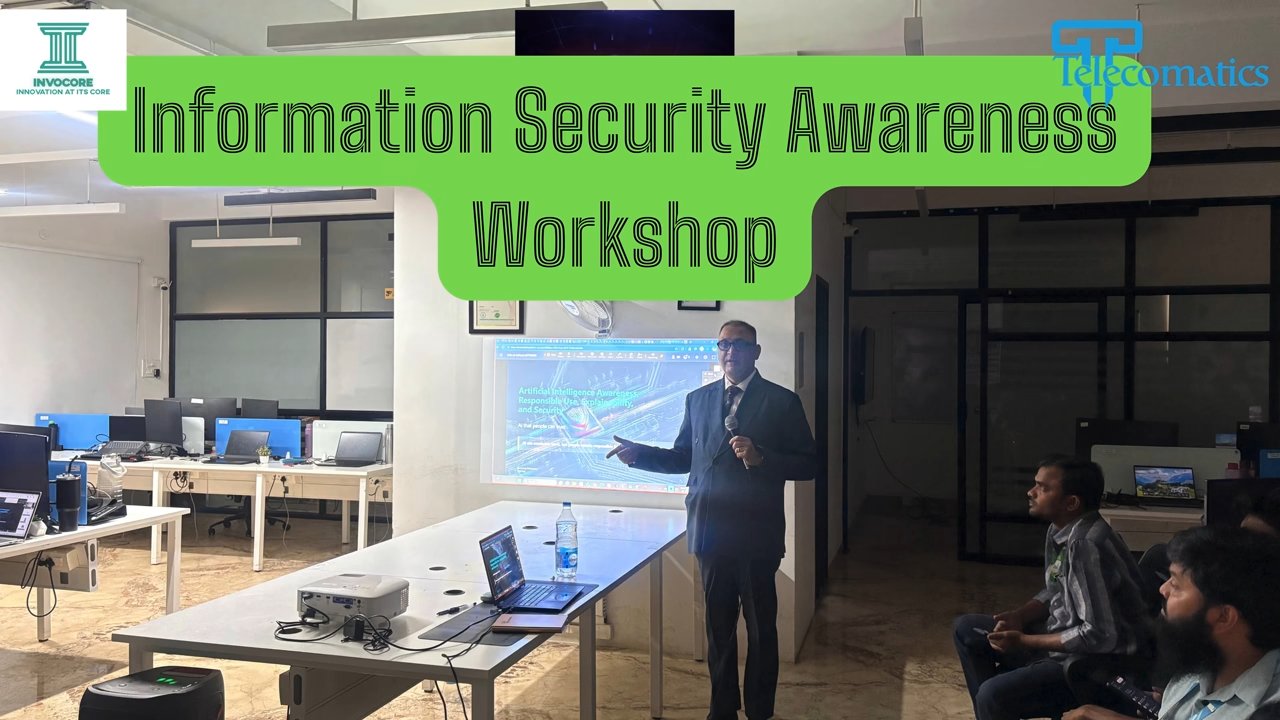
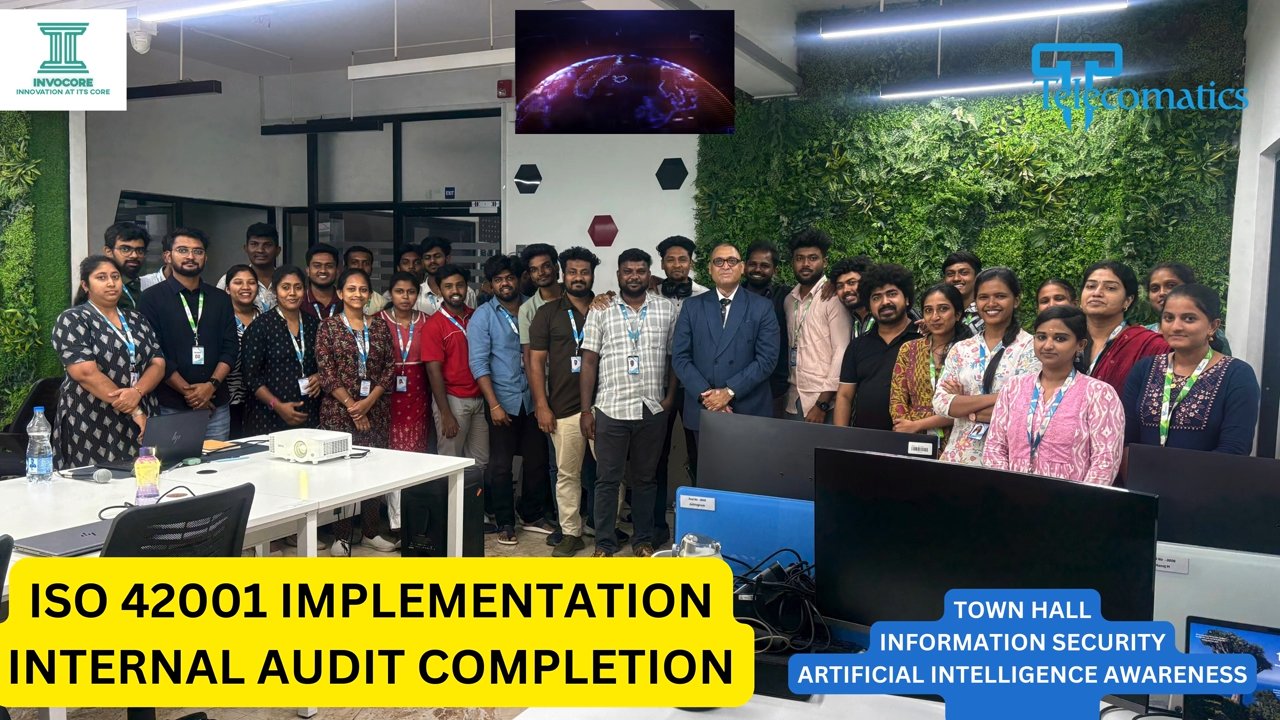
Telecomatics Technologies: from ISO 27001 certification to responsible AI
A technology company in Coimbatore, India, working with Invocore across consulting, implementation, internal audit and training. Information security came first; ISO/IEC 42001 AI governance followed on the same foundations.
- ConsultingISMS kickoff and a full gap assessment against ISO/IEC 27001:2022.
- ImplementationMore than 140 policies, procedures and registers, built with the team.
- CertificationISO/IEC 27001:2022 certification by an NABCB-accredited certification body.
- Internal auditOngoing quarterly internal audits to keep the ISMS effective.
- AI governanceISO/IEC 42001 AI management system implemented and internally audited.
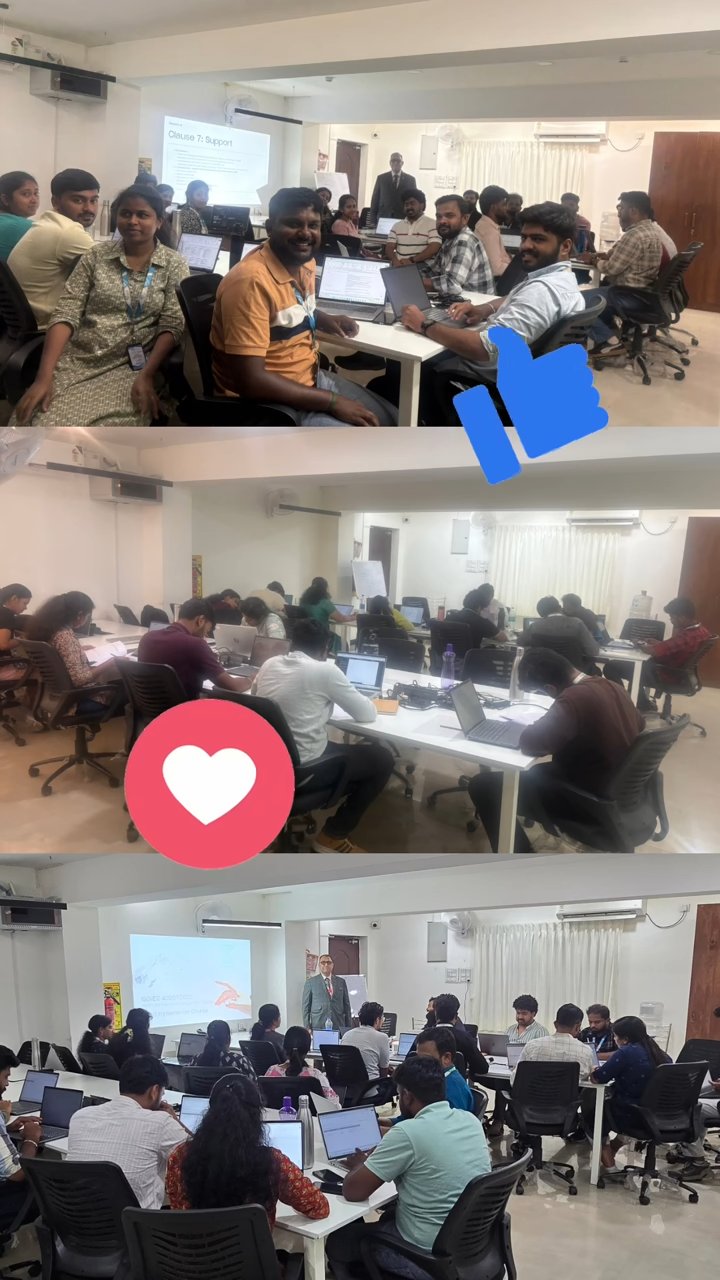
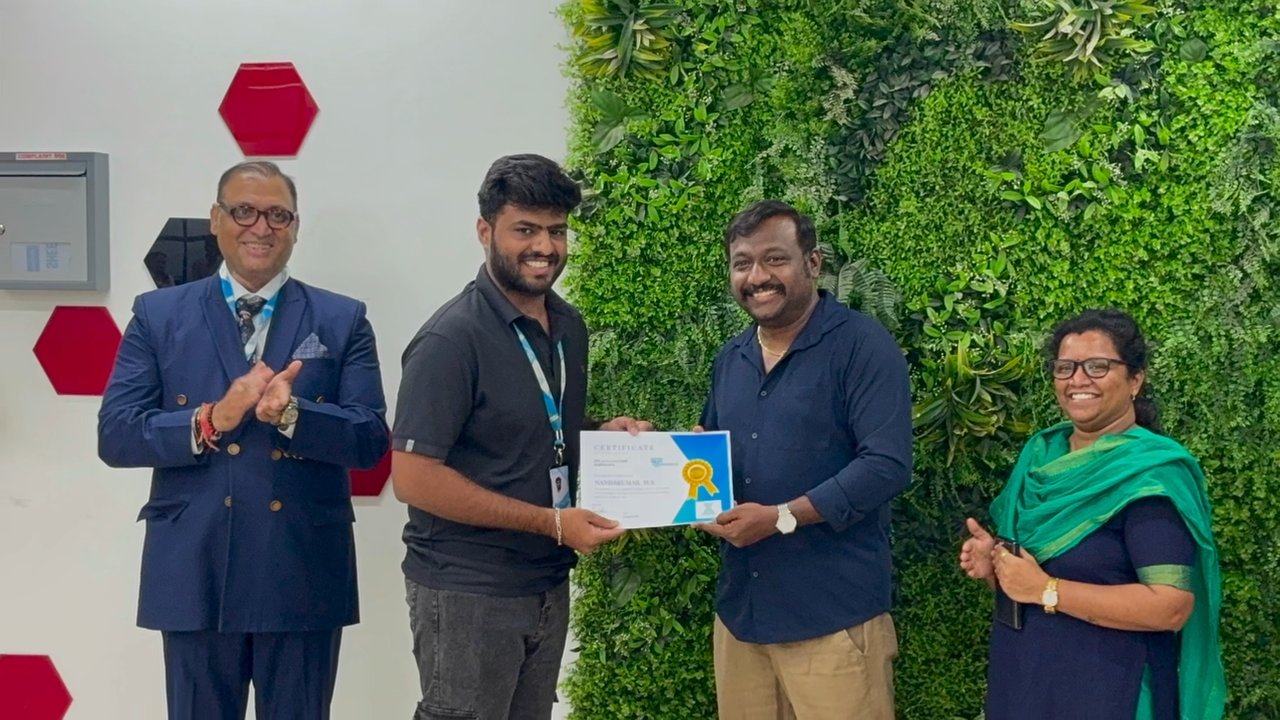
- TrainingISO/IEC 42001 Lead Implementer and Lead Auditor programmes, plus awareness for all staff.
Get in touch
Discuss your requirement
Tell us about your organisation and goals. A senior consultant will reply, usually within one working day.
Prefer to talk now? WhatsApp +91 98108 17659 or info@invocore.org
