
Services / Consulting & Implementation
ISO/IEC 42001 · AI Governance
Govern AI responsibly, and show it
Implement an AI management system aligned to ISO/IEC 42001: AI policy, AI risk and impact assessment, controls across the AI lifecycle, and audit readiness.
How an engagement runs
- DiscoverAI inventory and context
- AssessAI risks and impacts
- GovernPolicy, roles and objectives
- ControlLifecycle controls
- ValidateInternal audit and review
No model ships without a gate
Risk and impact assessment is built into the lifecycle, so every AI system is checked before it reaches people.
Responsible AI is a management discipline. Without owners, controls and evidence, it remains an intention.
Dr. Sanjay Vaid, Invocore
AI is moving faster than governance
Organisations building or using AI need to show customers, boards and regulators that AI is used responsibly. ISO/IEC 42001 is the international standard for an AI management system, and it gives a structured way to manage AI risk, transparency and accountability.
The challenge
Why this matters now
AI has moved from experiments to everyday operations. Teams use generative AI to write, code and analyse; products embed models that make or shape decisions about customers. In many organisations nobody can say with confidence which AI systems are in use, what data they rely on or who is accountable when they go wrong.
ISO/IEC 42001 is the first international management-system standard for AI. It gives organisations a structured way to set AI policy, assess risks and impacts, control the AI lifecycle and demonstrate responsible use to customers, boards and regulators. It also fits alongside ISO/IEC 27001 and 27701, so governance builds on what you already have.
Rapid AI adoption
Generative AI tools have spread across teams faster than policies and controls.
Emerging regulation
AI regulation, such as the EU AI Act, and sector guidance are raising expectations for transparency and accountability.
Customer scrutiny
Enterprise buyers increasingly ask how suppliers govern AI in their products and services.
Quick self-check
How ready are you?
Answer four questions leaders ask us. Your result appears instantly; nothing is stored or sent.
Do we know every AI system we build, buy or use?
Who is accountable when an AI system makes a harmful decision?
How do we assess bias, privacy and reliability before deployment?
Can we show customers and regulators that our AI is governed?
What we deliver
Capabilities
AI inventory
A register of AI systems you build, buy and use, with owners and purposes.
AI policy and objectives
Clear principles and responsibilities approved by leadership.
AI risk assessment
Identify and treat risks such as bias, privacy, security and reliability.
AI impact assessment
Assess effects on individuals, groups and society before deployment.
Lifecycle controls
Data, development, testing, deployment and monitoring controls aligned to Annex A.
Internal audit
Independent internal audit and readiness for certification.
Interactive
Explore the framework
Select any part of the diagram to see what it covers.
Selected
Context
Understand where and how you develop, provide or use AI, and who is affected.
Leadership
Top management sets AI policy, roles and accountability.
Planning
Assess AI risks and impacts and set objectives for responsible AI.
Operation
Apply controls across the AI lifecycle, from data to deployment and monitoring.
Evaluation
Monitor AI performance, audit the system and review results.
Improvement
Act on findings and incidents to improve AI governance.
Our approach
How we work with you
A clear, staged path from first assessment to lasting capability.
Step 1
Discover
AI inventory and context
Step 2
Assess
AI risks and impacts
Step 3
Govern
Policy, roles and objectives
Step 4
Control
Lifecycle controls
Step 5
Validate
Internal audit and review
Why Invocore
What sets us apart
Senior, practitioner-led advice that holds up in front of auditors, boards and customers.
Governance meets delivery
We embed AI risk and impact checks into how AI is built and bought, not as a separate bureaucracy.
Integrated management systems
Designed to work with ISO/IEC 27001 and 27701, avoiding duplicate processes.
Board-level clarity
Clear reporting on AI value, risk and compliance for leadership.
Engagement models
Start where you are
Begin with a focused first step and expand as value is proven.
Assess
AI governance gap assessment against ISO/IEC 42001 with a roadmap.
Fees on enquiry
Implement
Full AI management system implementation to audit readiness.
Fees on enquiry
Sustain
Ongoing AI governance support, or our Chief AI Officer as a service.
Fees on enquiry
Deliverables
What you receive
- AI system inventory and ownership register
- AI policy and objectives
- AI risk assessment and treatment plan
- AI system impact assessments
- Lifecycle controls mapped to Annex A
- Supplier and third-party AI checklist
- Internal audit report and readiness summary
Outcomes
What changes for you
- A complete AI inventory with accountable owners
- AI risk and impact assessments built into delivery
- Controls across the AI lifecycle, aligned to ISO/IEC 42001
- Evidence of responsible AI for boards, customers and auditors
Who we work with: AI product companies, Enterprises adopting generative AI, BFSI and healthcare, IT services and Public sector.
Frequently asked questions
Can ISO 42001 be combined with ISO 27001?
Yes. Both follow the same management-system structure, so many processes can be shared.
We only use third-party AI tools. Does 42001 apply?
Yes. The standard covers organisations that provide or use AI systems.
Do you help with AI policy only?
Yes. A standalone AI use policy is available through our Policy development service.
Client success story
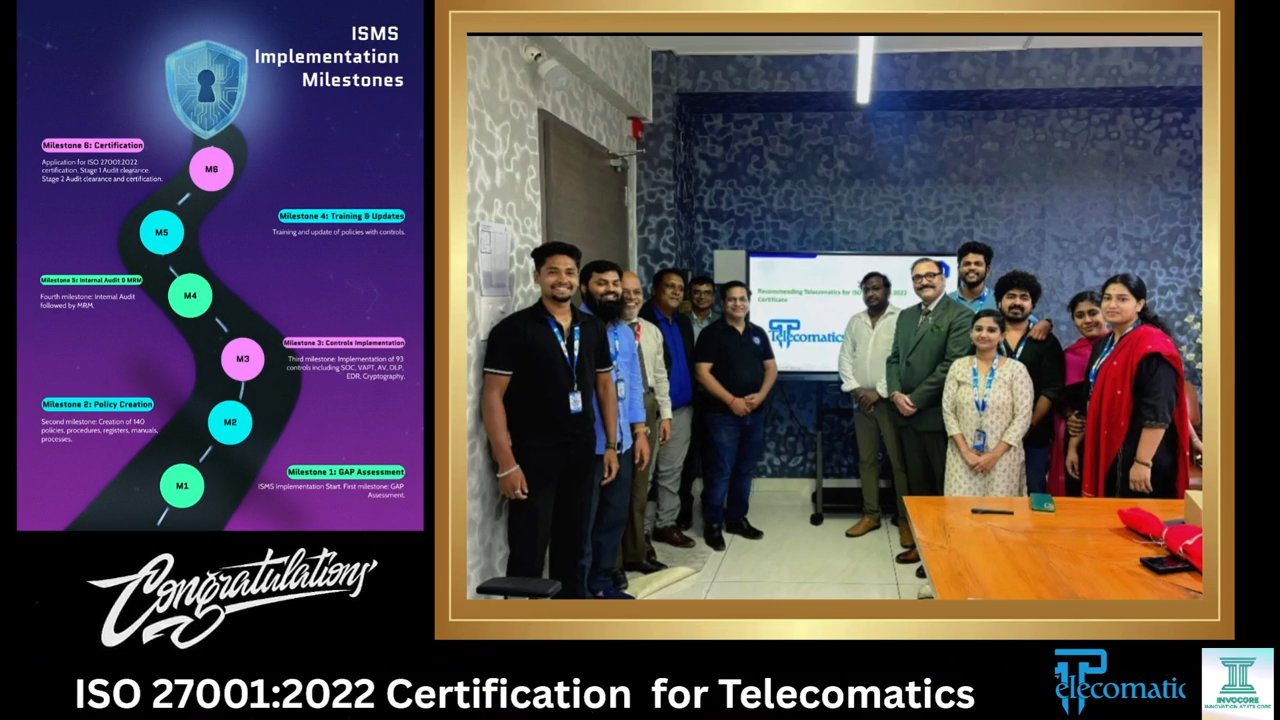
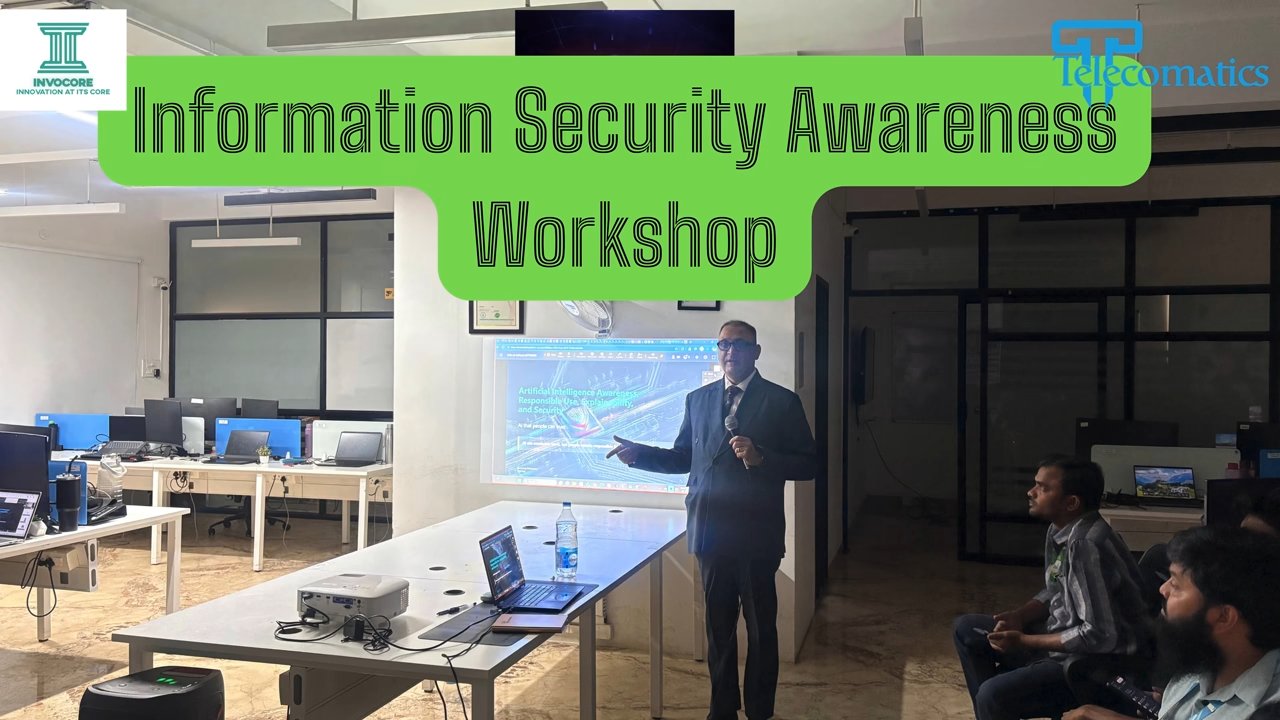
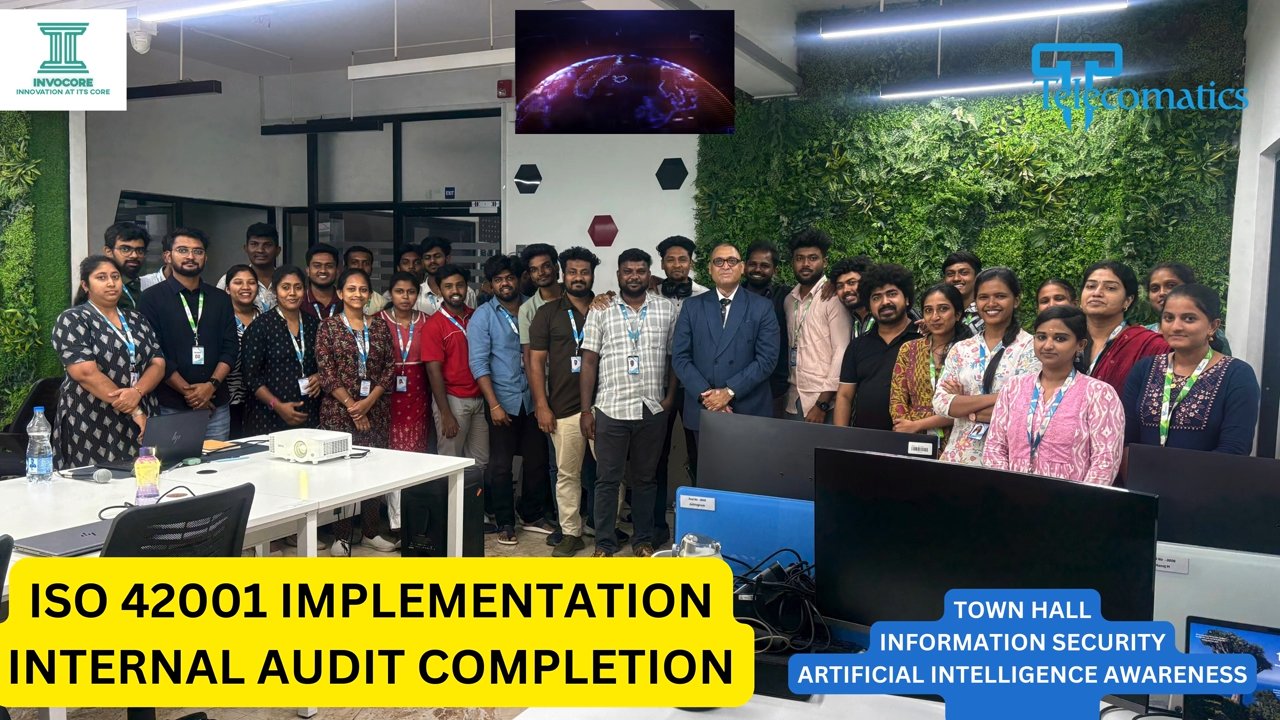
Telecomatics Technologies: from ISO 27001 certification to responsible AI
A technology company in Coimbatore, India, working with Invocore across consulting, implementation, internal audit and training. Information security came first; ISO/IEC 42001 AI governance followed on the same foundations.
- ConsultingISMS kickoff and a full gap assessment against ISO/IEC 27001:2022.
- ImplementationMore than 140 policies, procedures and registers, built with the team.
- CertificationISO/IEC 27001:2022 certification by an NABCB-accredited certification body.
- Internal auditOngoing quarterly internal audits to keep the ISMS effective.
- AI governanceISO/IEC 42001 AI management system implemented and internally audited.
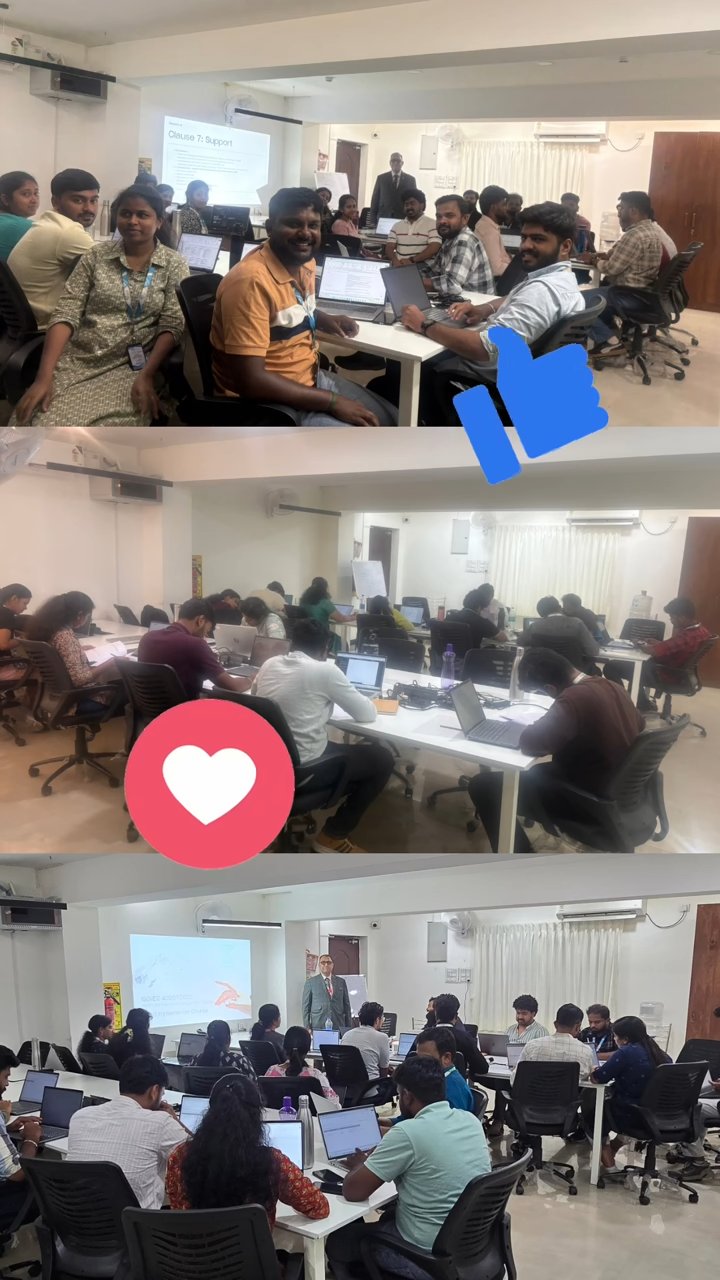
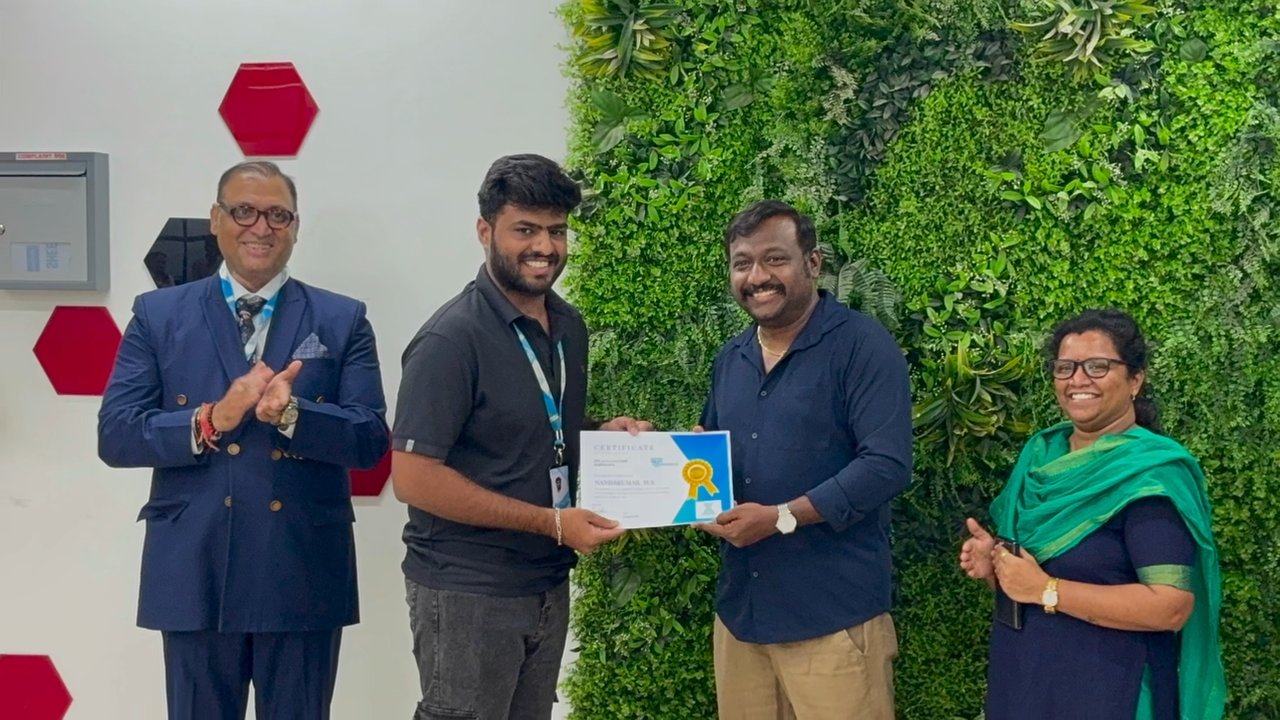
- TrainingISO/IEC 42001 Lead Implementer and Lead Auditor programmes, plus awareness for all staff.
Get in touch
Discuss your requirement
Tell us about your organisation and goals. A senior consultant will reply, usually within one working day.
Prefer to talk now? WhatsApp +91 98108 17659 or info@invocore.org
